1-Visitor
Mar 23, 2015 8:28 PM UTC
Solved

Sharing a Query


I have a set of queries that are Admin queries and a shared to only two groups. One of them is NOT the everyone group. Why then when I login on as a user not in either of those groups am I still able to see these queries? On page 158 of the 2009 Integrity User Guide it says:

3 Click the Sharing tab. The Sharing panel displays.

 Click Choose Principals and use the data filter to select the principals (users and groups) that you want to share your query with.

NOTE  Only the groups you add to the Shared With list can see your query. 
    DanR.Answer
    1-Visitor
    Mar 24, 2015 3:26 PM UTC

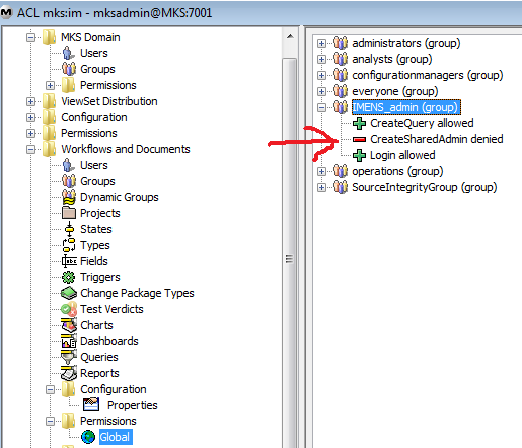
    I discovered the issue. Under "Workflows and Documents" > "Permissions" > "Global" I had a group with the "CreateSharedAdmin" set to allowed. Once I changed it to deny the shared queries in question were no longer visible.

    mks.png

    4 replies

    16-Pearl
    Mar 24, 2015 9:04 AM UTC
    I have a set of queries that are Admin queries and a shared to only two groups. One of them is NOT the everyone group.

    ... but the other one is.

    So basically you share with the group "everyone" and explains your systems behavior pretty well.

    Translate
    DanR.1-VisitorAuthor
    1-Visitor
    Mar 24, 2015 11:38 AM UTC

    But I am NOT sharing with the everyone group because I do not want everyone to see these queries.

    Translate
    DanR.1-VisitorAuthorAnswer
    1-Visitor
    Mar 24, 2015 3:26 PM UTC

    I discovered the issue. Under "Workflows and Documents" > "Permissions" > "Global" I had a group with the "CreateSharedAdmin" set to allowed. Once I changed it to deny the shared queries in question were no longer visible.

    mks.png

    Translate
    16-Pearl
    Mar 24, 2015 5:26 PM UTC

    Hi Dan,

    I'm glad that worked out. I think you might want to just unset that ACL, though: If you have a user who is a member of that group and a member of a group which does have CreateSharedAdmin allowed, they won't be able to create Admin objects unless they're granted CreateSharedAdmin at the user level, because in a conflict at the same level between allowed and denied, denied wins.

    -Kael

    Translate