
Security on Google Maps extension
Hello all,
I modified the Google MAps extension to use the HeatMaps API's and create a heatmap based on some data input. It is working well but I have a questions regarding security: in order to make the authentication i changed the metadata.xml file from the extension to include the AppKey that is required for using these APIs.
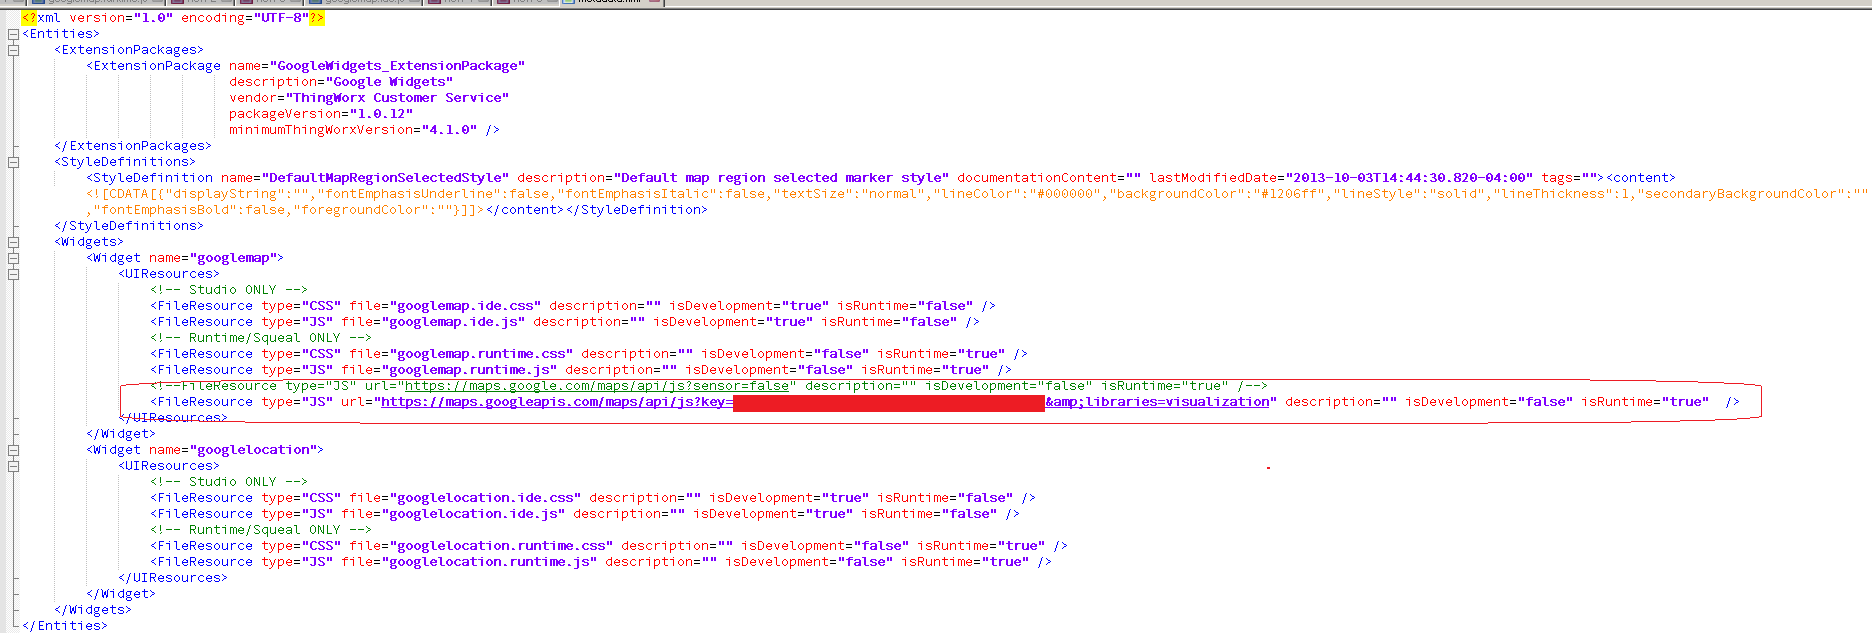
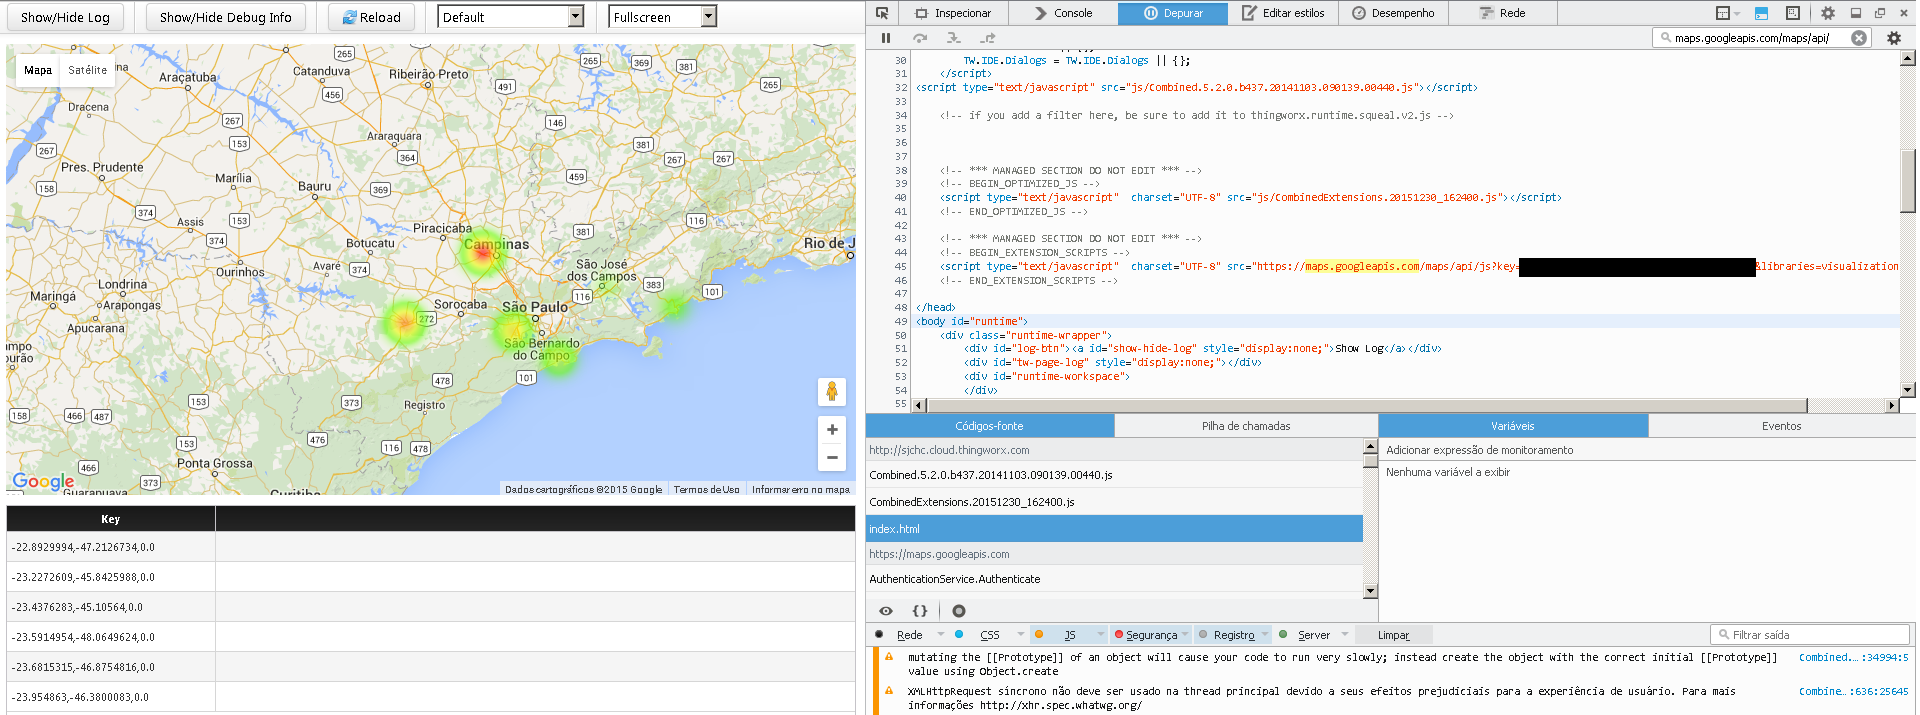
What happens is that when I run the Mashup, the AppKey shows up in the developer console, which is definitely not secure.As this API usage has a quota, in case the key leaks it can create unwanted billing. It is possible to define which URLs are allowed in the key configuration but I still do not feel comfortable on publishing the AppKey out there.
Does anyone have an idea of how I could secure this information?
Cheers
Ewerton